The High Cost of Legacy AI Compliance Audits#
When enterprise leadership realizes that employee use of ChatGPT, Claude, and internal RAG pipelines poses catastrophic regulatory and security risks, the default corporate reflex is to solicit proposals from legacy management consulting firms or the Big-4 accounting giants.
The resulting proposals follow a predictable, exorbitantly expensive pattern: - Timeline: 6 to 10 weeks of discovery interviews, stakeholder workshops, and spreadsheet circulations. - Staffing: Senior partners sell the engagement, while junior analysts copy-paste generic templates. - Price Tag: Ranging from $25,000 to $65,000 for initial assessments, with ongoing advisory retainers exceeding $8,000 per month. - Deliverable: A dense, 90-page PDF document summarizing theoretical privacy risks without committing a single line of protective code or eliminating a single live vulnerability.
For fast-moving technology companies, SaaS startups, and digital agencies, this traditional advisory model is not only financially prohibitive—it is technically obsolete.
> A 90-page PDF report does not stop an employee from pasting customer credit cards or Israeli ID numbers into an AI prompt tomorrow morning. Regulators and courts penalize real data breaches, not paper policy deficiencies.
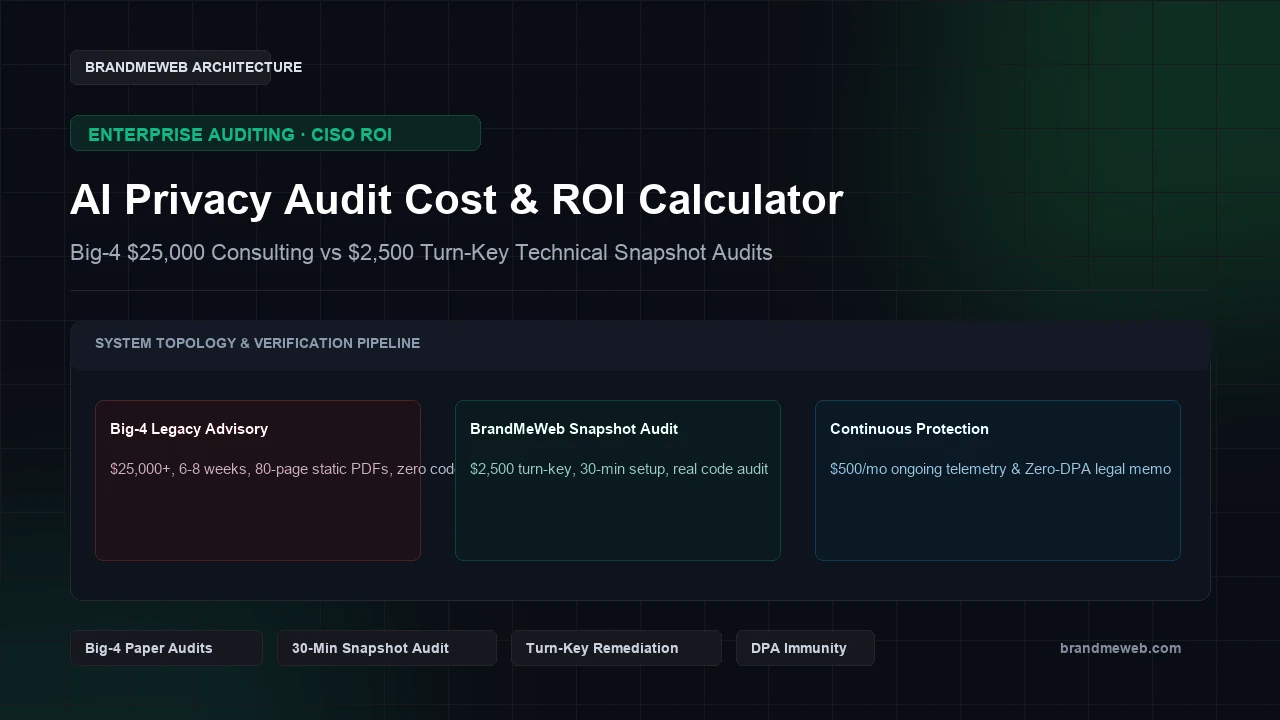
Comprehensive Economic Breakdown: Comparing Consulting Models#
Examining the three primary approaches to enterprise AI privacy auditing reveals stark differences in cost, execution speed, and practical remediation:
┌────────────────────────────────────────────────────────────────────────┐
│                     THE 10X ROI MULTIPLIER OF TECHNICAL AUDITING       │
├─────────────────────────┬──────────────────────┬───────────────────────┤
│ Big-4 Advisory:         │ BrandMeWeb Audit:    │ Immediate Financial   │
│ $25,000 expense,        │ $2,500 investment,   │ Benefit:              │
│ 8 weeks delay,          │ 48h delivery,        │ Save $22,500 cash,    │
│ zero technical fixes    │ full code protection │ eliminate fines today │
└─────────────────────────┴──────────────────────┴───────────────────────┘
Calculating the ROI of Preventive AI Sanitization#
Evaluating the return on investment of an enterprise AI privacy audit requires balancing the cost of preventive verification against statutory downside exposure:
- 1Statutory Regulatory Fines:
- 2Under Israel Amendment 13 to the Privacy Protection Law, administrative sanctions reach up to 3.2 million ILS (~$860,000 USD) per corporate infraction. Under European GDPR, maximum fines reach €20 million or 4% of annual global turnover.
- 3- *Downside Protection Ratio*: A $2,500 audit provides a 340:1 financial insurance ratio against statutory administrative penalties.
- 1Statutory Damages Without Proof of Injury:
- 2Under Amendment 13, class-action plaintiffs and individual users can claim up to 10,000 ILS per violation without demonstrating actual damages. A single customer database leak of 500 records exposes an enterprise to 5,000,000 ILS in immediate statutory liability.
- 1Subprocessor DPA Negotiation Overhead:
- 2Drafting, redlining, and negotiating customized Data Processing Agreements across multiple AI tool vendors typically consumes 20 to 40 hours of specialized legal counsel billable time ($400–$800/hr), costing $8,000 to $32,000 annually.
- 3- Deploying the Zero-DPA architecture eliminates vendor subprocessor liability entirely, saving thousands in annual legal review fees.
> Real security is binary: either sensitive cleartext data crosses your network boundary, or it does not. By enforcing client-side ZTDS sanitization, you eliminate the technical condition that triggers regulatory liability.
How the BrandMeWeb $2,500 Snapshot Audit Operates#
The BrandMeWeb AI Compliance & Privacy Audit operates on an engineering-first model engineered for immediate turnaround:
- 1Phase 1: Automated Discovery & Risk Mapping (Day 1):
- 2We map all internal AI touchpoints, developer IDE workflows (Cursor, Copilot), customer support chat integrations, and background RAG pipelines.
- 1Phase 2: Technical Remediation & ZTDS Invariant Verification (Day 2):
- 2We implement in-memory sanitization rules, deploy local regex filters, and verify zero cleartext network egress in device memory.
- 1Phase 3: Issuance of Zero-DPA Compliance Memorandum & DPIA (Day 2):
- 2We deliver an executive-level, audit-ready compliance package:
- 3- Formal Data Protection Impact Assessment (DPIA) satisfying Israel Amendment 13 and GDPR requirements.
- 4- Zero-DPA Legal Memorandum certifying zero external personal data transmission.
- 5- Board-ready executive summary for investors, enterprise clients, and cyber insurance underwriters.
Frequently Asked Questions (FAQ)#
What documentation does our company receive at the conclusion of the audit? You receive a comprehensive technical and regulatory package: an official Zero-DPA Compliance Memorandum, a formal GenAI Privacy Impact Assessment (DPIA), a technical architectural diagram of your sanitized AI pipelines, and a developer implementation checklist.
Is the $2,500 snapshot audit sufficient for SOC 2 and ISO 27001 AI audits? Yes. Modern SOC 2 Type II and ISO 27001 auditors specifically scrutinize how organizations manage third-party AI subprocessor risks and employee prompt leakage. The ZTDS Zero-DPA certification provides concrete cryptographic evidence of data isolation.
How do we get started? Test your prompts right now using our free [AI Data Leak Checker](/en/tools/ai-data-leak-checker), or contact our engineering team to book your turn-key [AI Compliance & Privacy Audit](/en/services/ai-compliance-privacy-audit).
Cost Comparison: Big-4 Advisory vs Turn-Key Engineering Snapshot
Select organization scale to calculate direct cost savings and SLA acceleration against legacy manual consulting.
- Timeline: 6 weeks
- Theoretical PDF without code audit
- Heavy manual staff interviews
- Senior engineering context switching
- Risk of missing IDE prompt leaks
- Complex vendor DPA negotiations
- Turn-key DPIA sign-off in 48 hours
- Zero Network Egress in device RAM
- $500/mo continuous verification