The K2view Benchmark: 87% of Companies Leak Data to AI#
According to K2view's comprehensive 2026 enterprise cybersecurity benchmark, 87% of global enterprises remain vulnerable to confidential data leakage into Generative AI models.
With over 471 million victim notifications recorded in H1 alone and Gartner forecasting that by 2029 the majority of privacy breaches will originate from AI inference attacks rather than static database dumps, corporate AI safety policies have failed.
> Prohibiting employees from using AI tools in corporate handbooks is ineffective. Employees copy-paste financial projections, customer records, and proprietary source code into ChatGPT and Claude to accelerate their workflows.
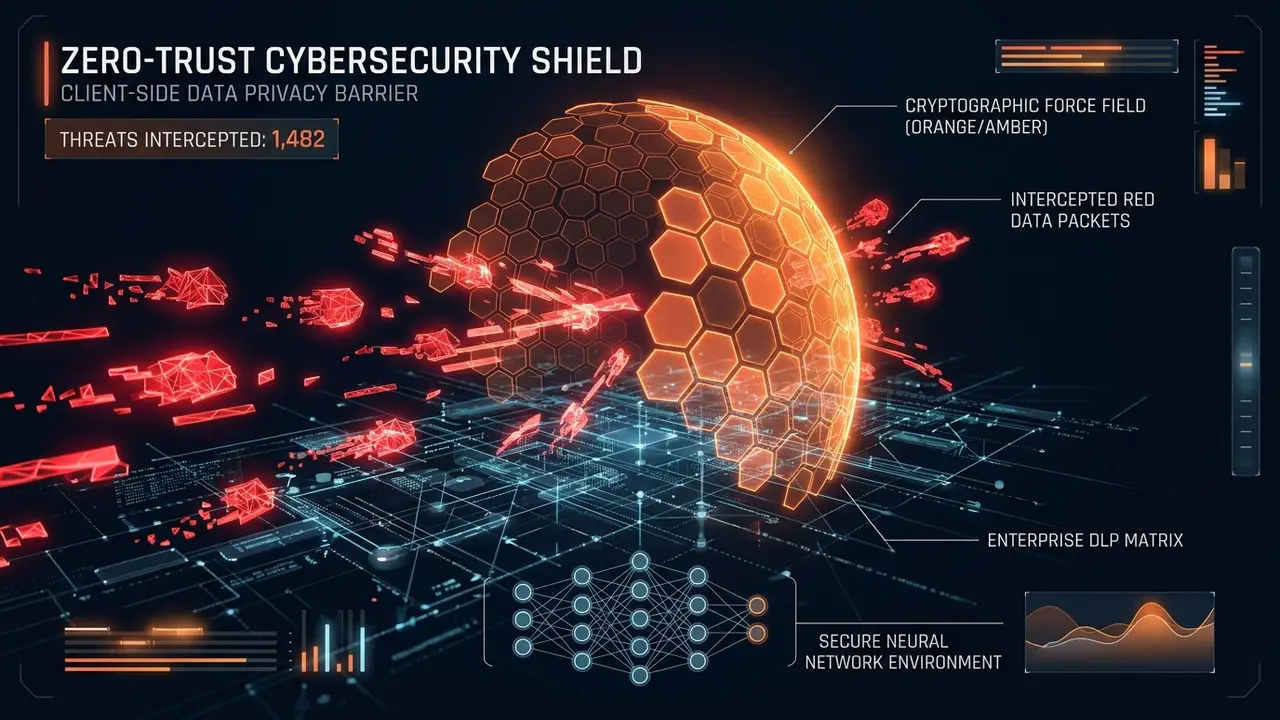
How Enterprise CISOs Deploy Zero-Trust Data Sanitization (ZTDS)#
- 1Enforce Endpoint Interception: Implement browser extensions and IDE plugins that automatically sanitize clipboard and input data before the network request is initiated.
- 2Equip Free Local Developer MCP Gateways: Deploy sandboxed in-memory Model Context Protocol (MCP) servers (
npx -y @privacyscrubber/mcp-server) so engineering teams safely connect Cursor and Claude Desktop to private repositories with zero cloud egress, backed by@privacyscrubber/sdk(free trial) on backend runtimes. - 3Maintain Cryptographic Audit Logs: Maintain tamper-proof local logs verifying that zero unmasked PII was transmitted to external AI endpoints.
> Empower employee productivity with AI by implementing client-side zero-trust sanitization rather than issuing futile bans.